Consent Management
The Viafoura consent management script is used to track if a user has consented for their current session to be shared.
Viafoura provides three options for integrating into various Consent Management Platforms (CMPs). We recommend using A. Transparency & Consent Framework (TCF) API integration as the most flexible but provide some options for non-compatible Consent Management Platforms. The options listed in order of recommendation are:
A. TCF API integration - This option is the most flexible and needs the least technical involvement as long as the CMP used is compliant with TCF API v2 or above.
B. Variable/Local Storage flag - This option requires some developer involvement and is less flexible than the first option. This option usually can be used in conjunction with cookie banners or similar CMPs.
C. Consent JavaScript file - This option is the most technical and the least flexibility. This option can be used with CMPs that can only block scripts from loading as a way to manage consent.
A. TCF API Integration
If the Consent Management Platform used supports TCF (Transparency & Consent Framework) API v2.0 and higher, Viafoura can integrate using the following steps.
Note Consent Management Platform needs to return correct gdprApplies response for regions where GDPR does not apply in order for this integration to work correctly.
To enable, follow these steps for each site that will use this integration:
- Include Viafoura as a vendor for the specified purposes in your CMP configuration.
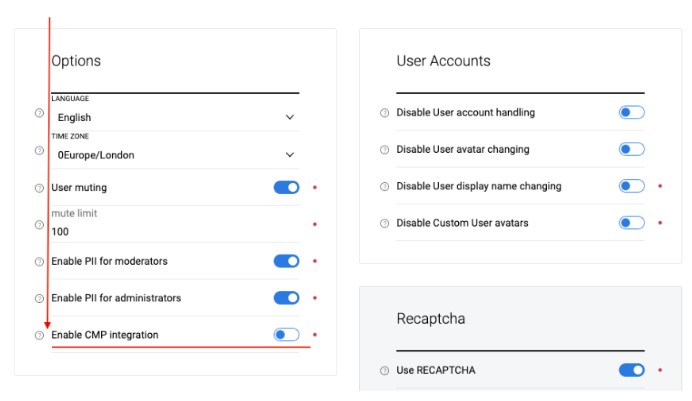
- Enable CMP integration under “General” settings in the Viafoura Admin Console:
- Reach out to your Viafoura CSM Viafoura to notify steps 1 & two of this integration are complete and Viafoura perform quick integration checks to confirm configuration.
B. Variable/Local Storage flag
This configuration provides less flexibility than TCF API and can be used in conjunction with both CMPs that don’t currently support TCF API v2 or above, as well as cookie banner integrations.
To enable this integration, your developers would need to execute the following JavaScript code before loading any Viafoura scripts. This code is as follows:
// Make vfConsent available or use existing one if already loaded
window.vfConsent = window.vfConsent || {};
window.vfConsent.flag = <CONSENT_VALUE>;
// Optionally set storeFlag to instruct our code not to store flag in localStorage
window.vfConsent.storeFlag = <IS_FLAG_VALUE_STORED>;
Replace <CONSENT_VALUE> with one of the values:
| Consent Value | Reason |
|---|---|
-2 | Will block all Viafoura products from loading until consent is given (not recommended). NOTE: this will only work if you are using our entry point . (https://cdn.viafoura.net/entry/index.js) |
-1 | Will load Viafoura products but blocks everything that falls outside of the functional category. (maps to IAB Purpose 1 and IAB Special Purposes 1 & 2) |
1 | Will load Viafoura products and allow some customization (maps to IAB Purposes 1, 10 & 11 and IAB Special Purposes 1 & 2) |
2 | Will load Viafoura products and, in addition to functional and customization, will allow data collection for analytics and customization. (maps to all purposes we use as perConsent Features ) |
NOTE: window.vfConsent.storeFlag = <IS_FLAG_VALUE_STORED>; is optional. You can use it and replace <IS_FLAG_VALUE_STORED> with false (Boolean) to instruct our code not to store flag value in localStorage. In that case you would need to run this code on every page until the user gives consent equivalent towindow.vfConsent.flag value of 1 or 2.
C. Consent JavaScript file
This option is the least recommended but is provided for cases where the only control option your CMP offers is blocking scripts from loading as a way to manage consent.
The Viafoura consent management script is used to track if a user has consented to their current session to be shared. It requires you to load an extra JavaScript file on your site(s) and then add it to your CMP as a script to block. This will ensure the Viafoura products will function (mapping to IAB Purpose 1 and IAB Special Purposes 1 & 2) while blocking any analytics or customization.
This will allow your users to be able to do things like read/edit comments even if they don't consent to being tracked.
To enable this integration, follow these steps for each site that will use this integration:
- Load the Viafoura Tracking Consent JavaScript file
Add the Tracking Consent script to the head of each of your pages on each site as early as possible, in accordance with your CMP's guidelines. Some CMPs insist on being the first thing loaded in thehead, and that any scripts you want blocked to be loaded directly afterwards.
The script's URL is https://cdn.viafoura.net/vftc/index.js.
<!DOCTYPE html>
<html>
<head>
...
<script type="text/javascript" src="https://cdn.viafoura.net/vftc/index.js"></script>
</head>
</html>
NOTE: This script needs to be in the head and not the body, so that your CMP can block it before it executes.
- Add Viafoura script to your Consent Management Platform (CMP)
In your CMP you will need to ensure thatvftc.jsis picked up and configured to be blocked when the user does not consent to being tracked. The steps to do this will be dependent on the CMP you are using. - Add viafoura's scripts as normal. If you are using the CDN entry point (
index.js) or originalvf-v2.js, nothing changes here. You want to continue loading that script as normal.
How it works
The extra JavaScript is called vftc - Viafoura Tracking Consent. This is a tiny piece of JS that you need to include on every page. When the script is not blocked by the CMP, then it will set a flag on sessionStorage called __vftc__. The rest of our JavaScript will be looking for this flag and that the vftc script was in the code of the page. When it does not find it, then it will not track the user.
How do I know that the script is working?
If the script is running and consent has been given to track, you will see a local storage value of "__vftc__": true. If there is no local storage value that means that our script has been blocked by your CMP. You can see that by looking at the markup where our script is and see if type=javascript/blocked has been added to it.
Check your setup
Use this check to confirm that Viafoura respects your readers' consent choices. It works with all three options above and takes about 5 minutes per site.
Before you start
- Use Google Chrome, and open a new Incognito window for each test so earlier consent choices don't carry over.
- Pick an article page that shows Viafoura comments.
- Test from a region where your consent banner appears. For example, if your banner only shows to readers covered by GDPR, test from the EU or UK.
Step 1: Reject test
- Open a new Incognito window and go to the article.
- Click Reject all (or your banner's equivalent) and reload the page.
- Open the browser console: Cmd + Option + J on Mac, or Ctrl + Shift + J on Windows.
- Paste the snippet below and press Enter. If Chrome warns you about pasting, type
allow pasting, press Enter, and paste again.
Step 2: Accept test
- Close the Incognito window and open a new one.
- Go to the same article, click Accept all, and reload the page.
- Open the console and run the snippet again.
Snippet
(function () {
  var w = window, done = false;
  var tcf = typeof w.__tcfapi === 'function', vfc = w.vfConsent;
  var vftc = document.querySelector('script[src*="vftc"]');
  var get = function (s, k) { try { return s.getItem(k); } catch (e) { return null; } };
  var report = function (d) {
    if (done) return; done = true;
    var out = ['Viafoura consent check - ' + location.hostname, ''];
    out.push('Method: ' + (tcf ? 'A. TCF API' : vfc ? 'B. window.vfConsent flag' : vftc ? 'C. vftc script' : 'None detected'));
    if (tcf) out.push('Viafoura (vendor 1138) consented: ' + (!d ? 'no answer from CMP' :
      d.gdprApplies === false ? 'n/a - GDPR does not apply here' :
      d.vendor && (d.vendor.consents[1138] || d.vendor.legitimateInterests[1138]) ? 'YES' : 'NO'));
    if (vfc) out.push('vfConsent flag: ' + vfc.flag + ' | storeFlag: ' + vfc.storeFlag);
    if (vftc) out.push('vftc script: ' + (vftc.type === 'javascript/blocked' ? 'blocked' : 'running') +
      ' | __vftc__: ' + (get(w.sessionStorage, '__vftc__') || get(w.localStorage, '__vftc__') || 'not set'));
    out.push('Viafoura analytics cookies (_vfa/_vfb/_vfz): ' + (/(^|; )_vf[abz]=/.test(document.cookie) ? 'PRESENT' : 'none'), '');
    var notes = [];
    if (!tcf && !vfc && !vftc) notes.push('No consent integration detected. See options A to C above.');
    if (tcf && vfc) notes.push('Both a TCF CMP and window.vfConsent were found. Contact your Viafoura CSM to confirm your setup.');
    if (vfc && [-2, -1, 1, 2].indexOf(vfc.flag) < 0) notes.push('Flag ' + vfc.flag + ' is not one of the documented values (-2, -1, 1, 2).');
    if (vfc && vfc.flag === -2) notes.push('Flag -2 blocks all Viafoura products until consent is given (not recommended).');
    out.push(notes.length ? 'Notes:\n- ' + notes.join('\n- ') : 'Notes: none');
    console.log(out.join('\n'));
  };
  if (!tcf) return report(null);
  setTimeout(function () { report(null); }, 3000);
  w.__tcfapi('addEventListener', 2, function (d, ok) {
    if (!ok || !d) return;
    report(d);
    if (d.listenerId != null) w.__tcfapi('removeEventListener', 2, function () {}, d.listenerId);
  });
})();
Step 3: Compare your results
| After Reject | After Accept | |
|---|---|---|
| Comments visible | Yes * | Yes |
| Viafoura analytics cookies | none | PRESENT |
| Viafoura (vendor 1138) consented (option A only) | NO | YES |
| vfConsent flag (option B only) | -1 | 2 |
__vftc__ (option C only) | not set | true |
| Notes | none | none |
* If you use flag -2, comments won't appear until consent is given. This is expected for that value.
_vfa, _vfb and _vfz are Viafoura's analytics cookies. See What cookies and device storage objects are used by Viafoura?.
If the check shows n/a - GDPR does not apply here, your CMP has told Viafoura that GDPR doesn't apply where you're testing. Run the check again from a region where it does.
If your results don't match the table, send your Viafoura CSM the article URL, the region you tested from, and screenshots of the console output from both tests.
Updated 6 days ago